Security Built by security-first engineers
AI stays outside. Your data stays in.
Before asking what a system can do, we ask who can reach it, what they can see, and what happens when someone tries to misuse it.
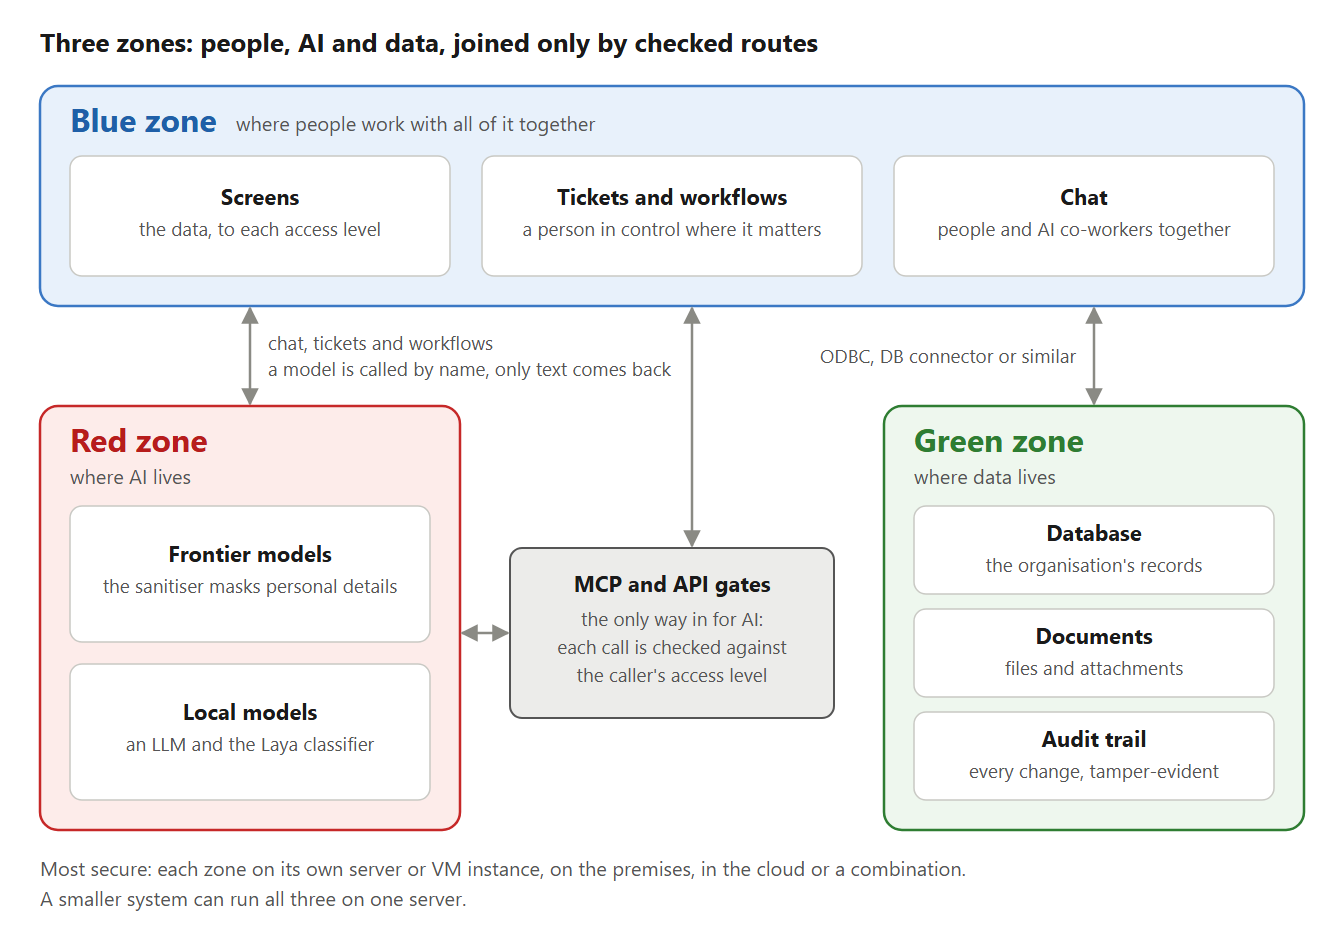
The architecture
Three zones, joined only by checked routes.
Six controls
What holds, even when the AI is wrong.
AI stays outside
Models never touch the data directly.
AI is a user
Two gates, an access level, every call logged.
AI never writes code
It describes. The platform builds.
Personal data is masked
Local model first. The sanitiser is set per co-worker today.
Sign-in is defended
Two-factor, attack blocking, hashed tokens.
Your premises or your cloud
Or both.
For your security review
What a reviewer asks first.
Can our auditor verify the audit log without your help?
Yes. The trail is a SHA-256 hash chain written by the database itself, so a change made outside the screens is recorded too.
If an agent is tricked by a prompt, what can it write, delete or read?
Only what its access level opens, through calls you have registered. The builder language has no delete command and returns no data.
When AI builds a screen, is any code generated?
No. The AI describes and the platform builds.
Where does personal data go before it reaches the model?
To a local model first. Before an outside model, through the sanitiser where it is set.
What stops stolen credentials being replayed?
Two-factor sign-in, blocking of an address under attack, and tokens stored only as hashes, so a copy of the database gives an attacker nothing to sign in with.
What is still open
We would rather you heard the gaps from us.
The sanitiser, required on every outside model.
Today it is set per co-worker.
- One stop per AI system
- Ask before a write
- Explanation on request